ShinyHunters has been one of the most damaging data extortion names of the past five years. Since 2020 it has claimed or been tied to breaches at Tokopedia, AT&T and Ticketmaster, the 2024 wave of Snowflake customer thefts, and the 2025 voice-phishing campaign against Salesforce customers. The name has outlived a lot of the people who used it. That raises a question nobody in that world can answer anymore: who actually owns it?
On October 5, a Telegram user named hasanbr0ker announced a new ShinyHunters-branded cell that he would lead “with the blessings of its former founders”. He also promised a new data leak site within the week. Two days earlier, the same account had posted “Rip Rey.”
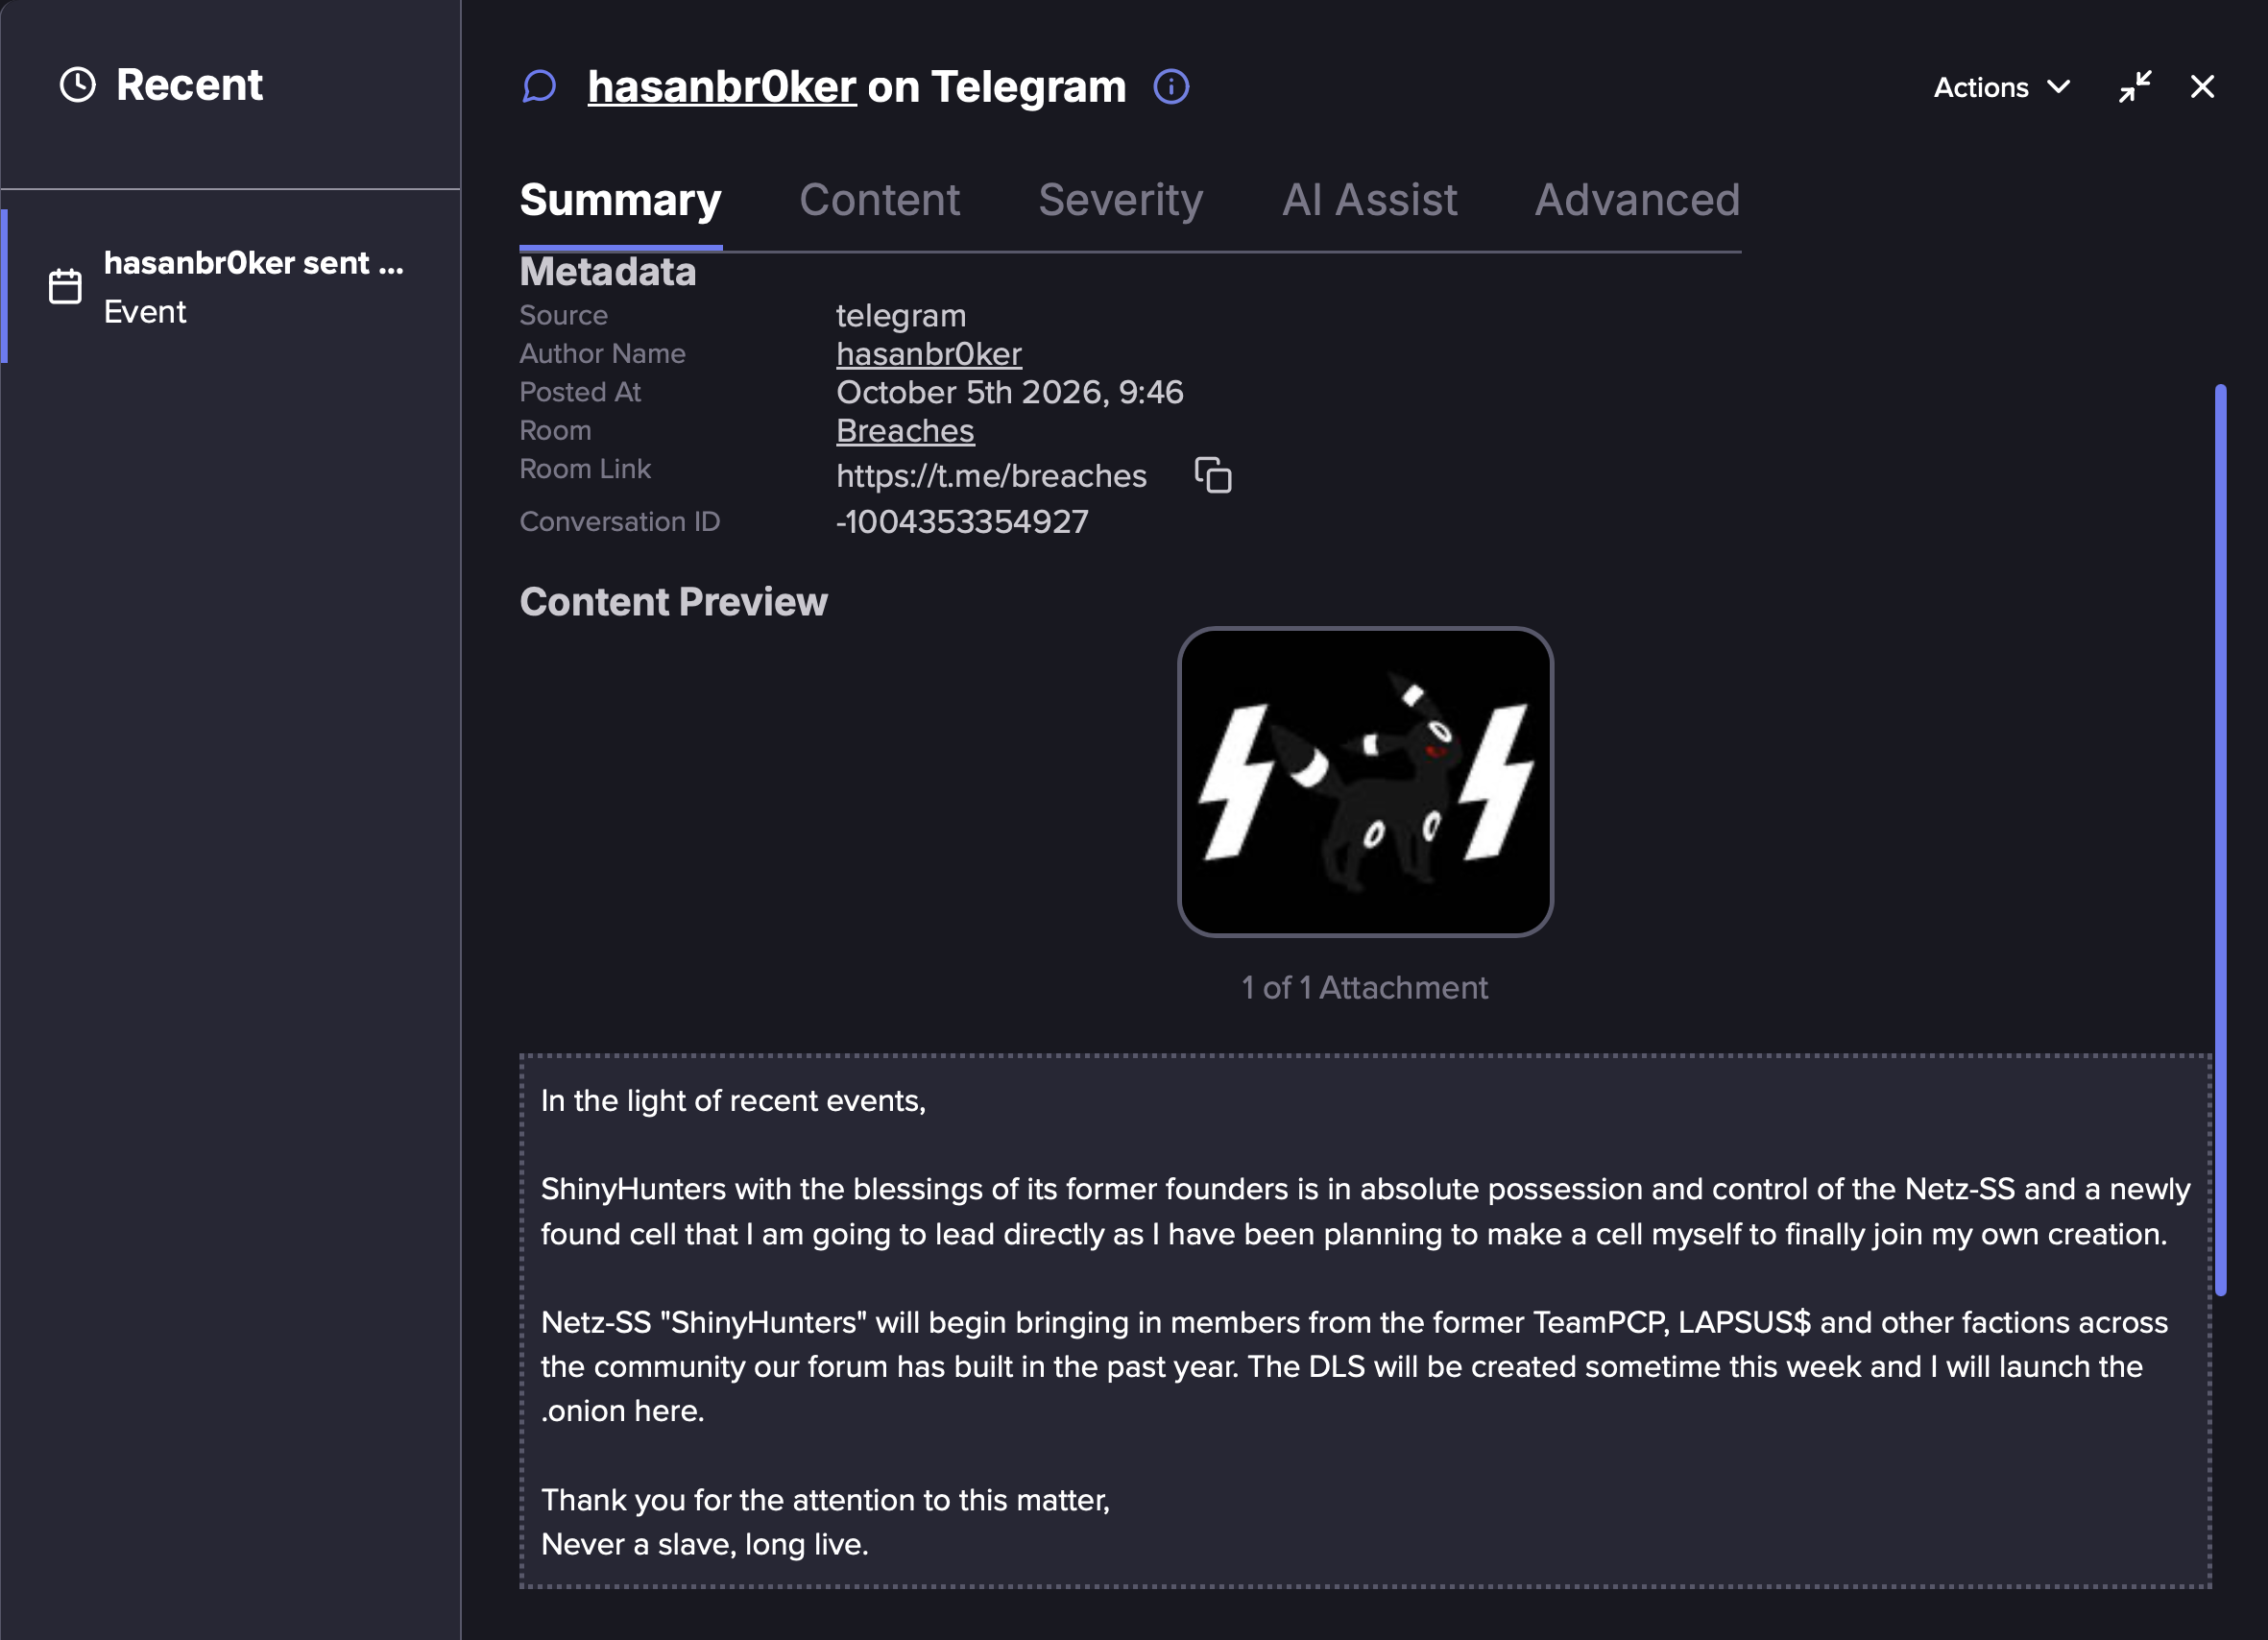
Look at the image he attached. It is Umbreon, the black Pokémon, standing between two SS sig runes, which matches the Netz-SS name. That choice matters, because hasanbr0ker is not the only one claiming ShinyHunters. For most of this year, two rival groups have both said they are the real thing: one operating mainly on Telegram, the other through the group’s onion leak site and the forums. More on that fight in a minute.
For now, know this: the loudest voice on the onion and forum side posts as umbreon_sh, a handle named after the same Pokémon. A logo is not attribution, and I would not hang anything on it alone. But hasanbr0ker chose the rival side’s mascot for Netz-SS, and that tells you which side he wants people to think he came from.
I can’t tell you whether hasanbr0ker is ShinyHunters. The keys and statements I examined do not establish who controls the name today.
I have been watching this name get passed around for most of 2026. On September 28, a criminal source told me Rey was in custody and that law enforcement in Jordan was operating his access. Reuters reported the arrest on October 3. Brian Krebs reported on October 7 how Rey took control of the brand after the Dutch arrest. He also quoted a claim that Rey bought the old forum’s PGP key. His blog does not identify which key. Since then, rival criminals have each published their own keys and statements and called the others fakes. The October 5 claim is the latest round of the same fight.
PART I: Who’s Got the Keys?
Every claim in this fight comes back to PGP keys. Whoever signs with the right key gets believed, so it matters a great deal who actually holds them.
In the Com, the loose online community where these criminals live, a PGP signature is how you prove you’re you. If a statement checks out against the admin’s known key, people treat it as real. At least, that’s how it’s supposed to work. I examined a statement bearing a December 17, 2025 signature timestamp from the BreachForums admin key. The key was created July 25, 2023.
Fingerprint: E80C1308A09EC1ADC418C3F02578988F69BCA3FC
I pulled the statement and ran the signature check myself. It came back good.
Around January 9, that private key leaked, and BleepingComputer reported the passphrase followed. In a forum post reported by The Register, the administrator said the key had been exposed in August 2025, four months before the date on the December signature.
The strongest authentication evidence in this fight used a key that other people may already have had, according to its owner. A good signature from E80C verifies the signed text and shows that someone used the corresponding private key. After January, that could be any number of people.
Before you treat a signature as proof of identity, check who has controlled the key. Once the private key has leaked, a valid signature cannot by itself identify who signed the message.
Everybody Gets a Key
Several different keys appeared in the dispute. A different key does not necessarily mean a different faction.
Figure 2 lays out the keys in order before I go through them one by one.
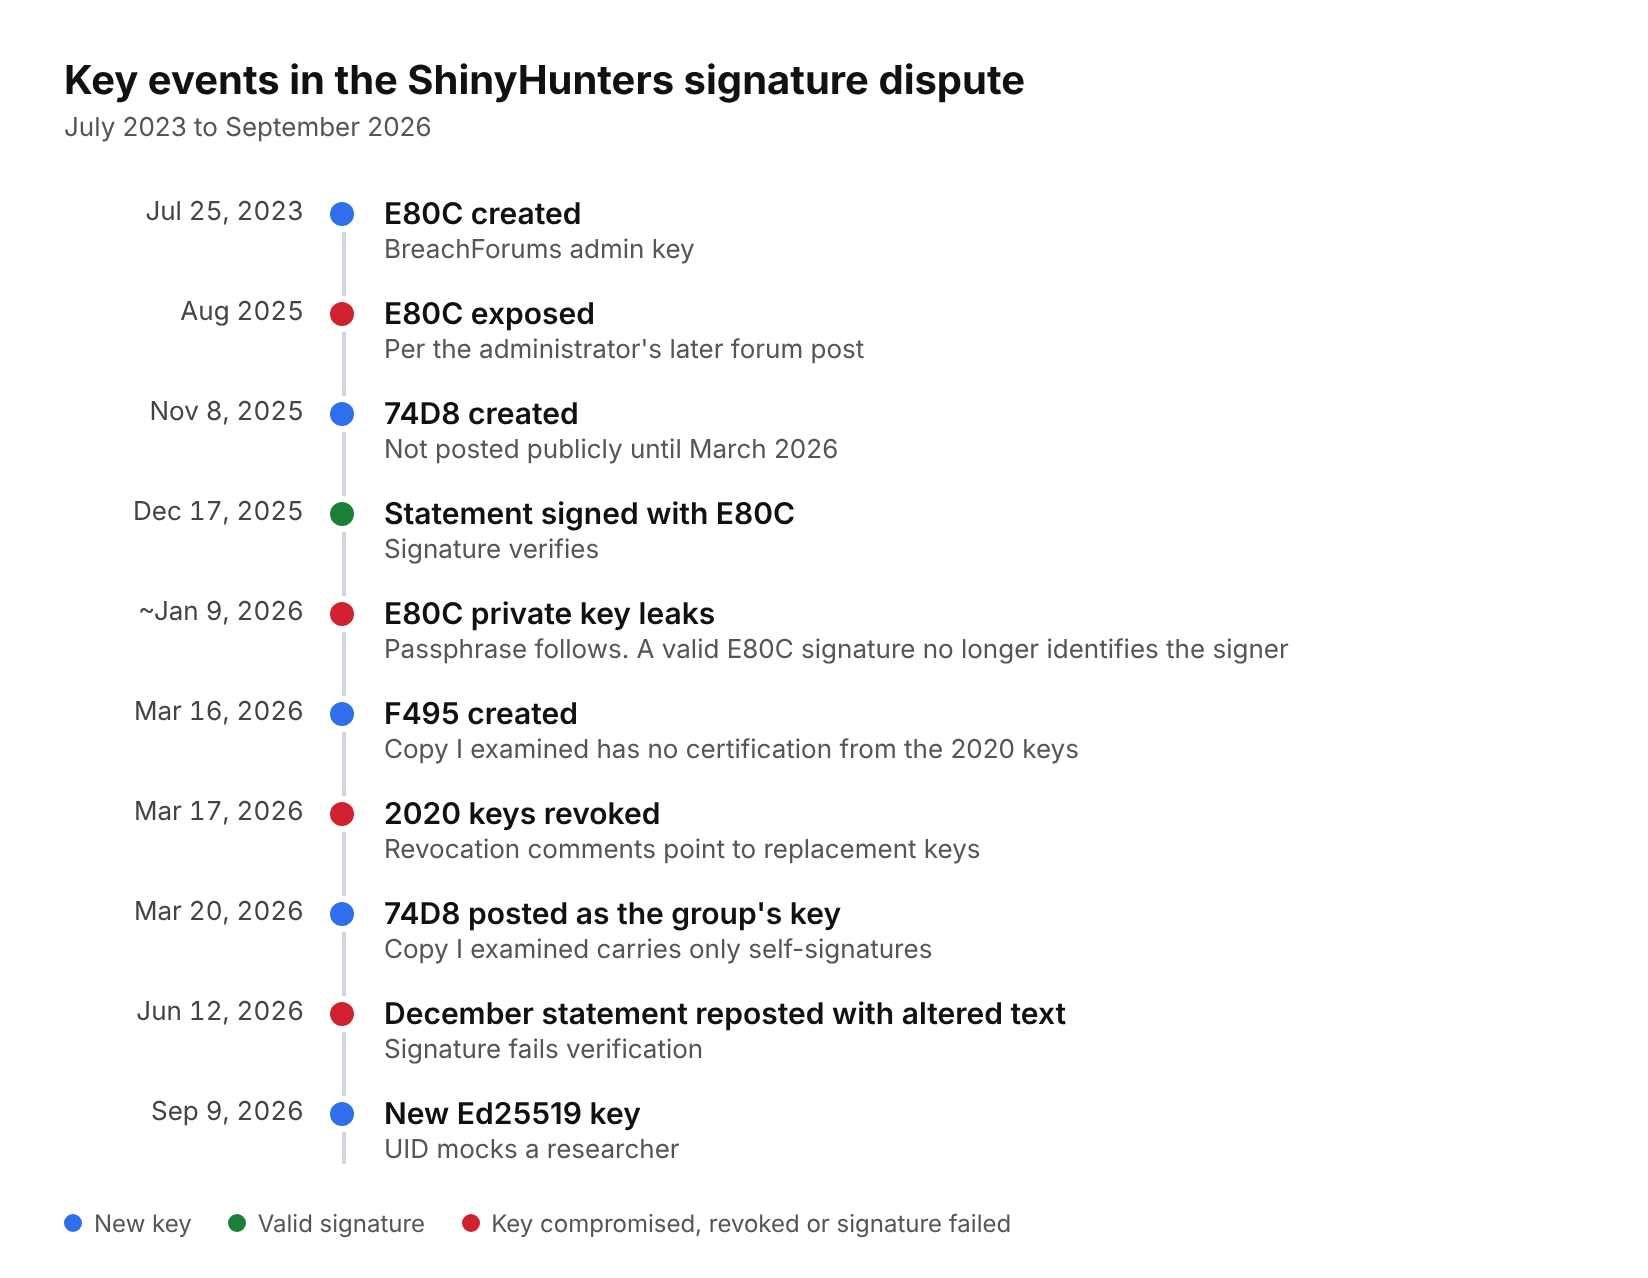
A key with fingerprint F4953411767DE71BEDCDABCB76F4E26F7A20978A has a creation date of March 16, 2026. The Hunter’s Ledger argued in April that this key was linked to the group’s original 2020 keys. I tested that on October 6. The F495 copy I examined carries no certification from either 2020 key (828537C1… and 1FC4D0B1…). Both 2020 keys were revoked on March 17, the day after F495 was created. A certification from an older key would sign off on the new key. The old keys’ revocation comments point to replacement-key locations. But the F495 copy I examined does not contain the certifications claimed in that account.
The other key material I tracked included:
- 5E00…
- 970E…, a recipient key ID in an encrypted message, not a verified statement signer.
- One using the Aegis name (28FF…).
- A September 9 Ed25519 key whose UID (the key’s name label) uses the address vinnytroia@pokemon[.]com, mocking researcher Vinny Troia. Trolling researchers by name is common in this crowd, and it tells you more about the key’s owner than it does about Vinny.
Another key had appeared earlier, on March 20: 74D8 9791 D24E 2F66 0086 E7F3 AEB0 1B21 3819 D67E. It was posted as the group’s key. I checked it. 74D8 was created November 8, 2025, four months before the March post I examined, under the name comparables@proton[.]me. The copy I examined contains self-signatures and no certification from E80C, F495 or the 2020 keys. A self-signature is made with that key’s own private key, rather than a different key.
The forged repost
At least one person knew signatures carry weight, because someone altered a signed statement and left the original signature attached.
On June 12, Telegram channel -1003920339685 reposted the December 17 statement with the original signature block attached. The text had been edited, including a handle (@myselft6040) that was not in the original. I ran the signature check on the June version, and it failed. The signature matched the original December text, not the edited one. Someone took a real signed statement, changed the words, and left the signature on, betting nobody would check.
PART II: Will the Real ShinyHunters Please Stand Up?
By spring there were two ShinyHunters, and each said the other was a fraud. One side worked out of Telegram channels, selling data and posting “official” statements. The other held the onion leak site and spoke through the forums. Both claimed the name, both claimed the founders’ blessing, and neither could prove it. Figure 3 maps the two sides.
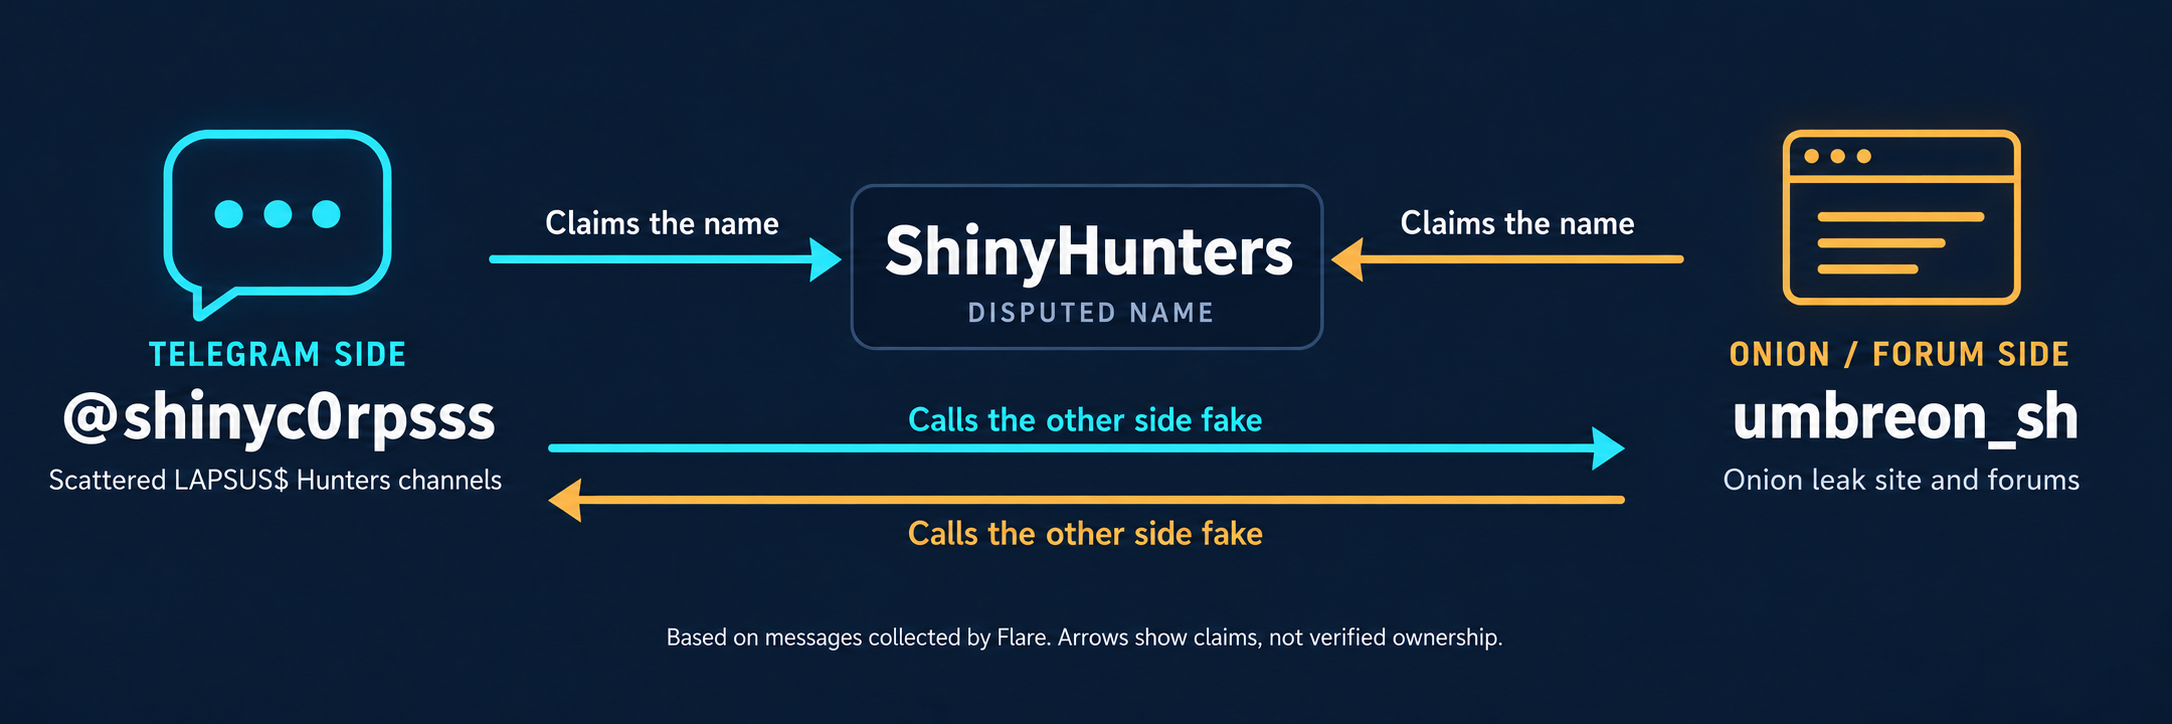
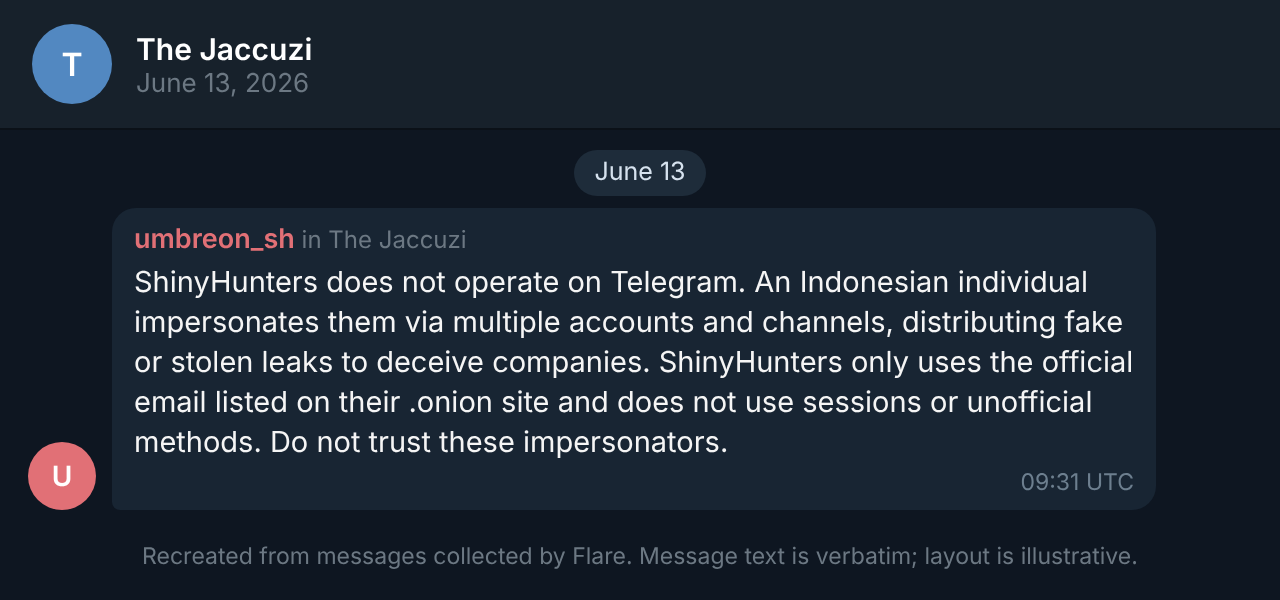
The Telegram side ran through @shinyc0rpsss and the Scattered LAPSUS$ Hunters channels. Escanors and Solonik posted alongside. The onion and forum side spoke through umbreon_sh. On June 13, that side told its audience the Telegram side was an “Indonesian individual” impersonating the group. The Telegram side made the same accusation in reverse.
The Telegram side also went after one person by name. Both his role and the claim that he holds the founders’ key rest on his rivals’ word, which is why I am not printing his name.
Starting April 20, its channels ran a sustained campaign against him. They accused him of using the ShinyHunters name for the Salesforce campaign Google tracks as UNC6040. They also accused him of running the onion blog as a copycat. On April 21 the Telegram side posted a BreachForums sale thread with his name in the title, calling him a ShinyHunters imitator.
On September 7 the Telegram side laid out the full story: before Hollow and YuroSH were arrested in France, the founders handed the PGP key to the unnamed man. The Telegram side said he still controls the onion blog. I counted more than 80 messages naming him across the channels Flare collects. Every one of them comes from the side that wants him discredited.
Everything must go!
BreachForums was advertised for $5,000 on March 22, $2,000 on July 27 and $3,000 on August 13 and August 27. That’s the only clearance sale I know of where the price went back up. The August 27 offer named bf[.]st and included its database, source code and infrastructure. These were asking prices, not verified sales, and I have not established that every offer covered the same assets. Honestly, I should have bought it just for the intel value.
Some background for anyone who has not followed this crowd. In June 2025, French police arrested several people they accused of running BreachForums, and press reports at the time named the handles involved, Hollow among them (The Register, June 25, 2025). Since then, the channels have treated Hollow as one of the founders who went down. The real name some of them attach to Hollow comes from a Telegram post, not from the authorities.
The ownership trail also runs through an account called Hollow. The name shows up in two places that should not overlap: among the alleged founders caught up in the June 2025 arrests, and as the owner account behind breachforums[.]rs. I haven’t established who was behind that later account. Meanwhile, another member, Figure, was publicly chasing Hollow over a $1,000 debt.
Show me the money!
This one stood out to me. This is a group that demanded millions from some of the biggest companies in the world. Its forum is on the clearance rack. And members are publicly chasing each other over a grand.
It’s just odd, but there’s a real point here. A crew that’s making money doesn’t fight over pocket change in public. Small debts turn into public beefs when cash is tight and nobody trusts anyone. Public beefs are how these crews come apart. Someone gets angry, someone gets doxxed, and the screenshots end up with researchers and law enforcement. If you track these groups, watch the petty fights. They tell you more about the health of the operation than any leak site does. And if any of those fights ever end with someone wanting to vent, I’m easy to find.
The roster that does not add up
ShinyHunters membership claims changed as often as the keys. On May 22 the Telegram side claimed an affiliate roster that included “Qillin” and HellCat. The list does not establish an affiliation with the Qilin ransomware operation. Anastasia, a former BreachForums owner, was presented as inside the group and outside it in posts weeks apart. On August 26 the Telegram side publicly disowned Sevy, who had been speaking for it. Months earlier, the same channels had listed Sevy alongside Rey and Aegis as a core member, so this was no fringe account. It was one of their own.
Don’t build attribution on a membership list from these channels. What the list says depends on who is posting it. Most of it is shit talking.
PART III: Rey Is Dead, Long Live Rey
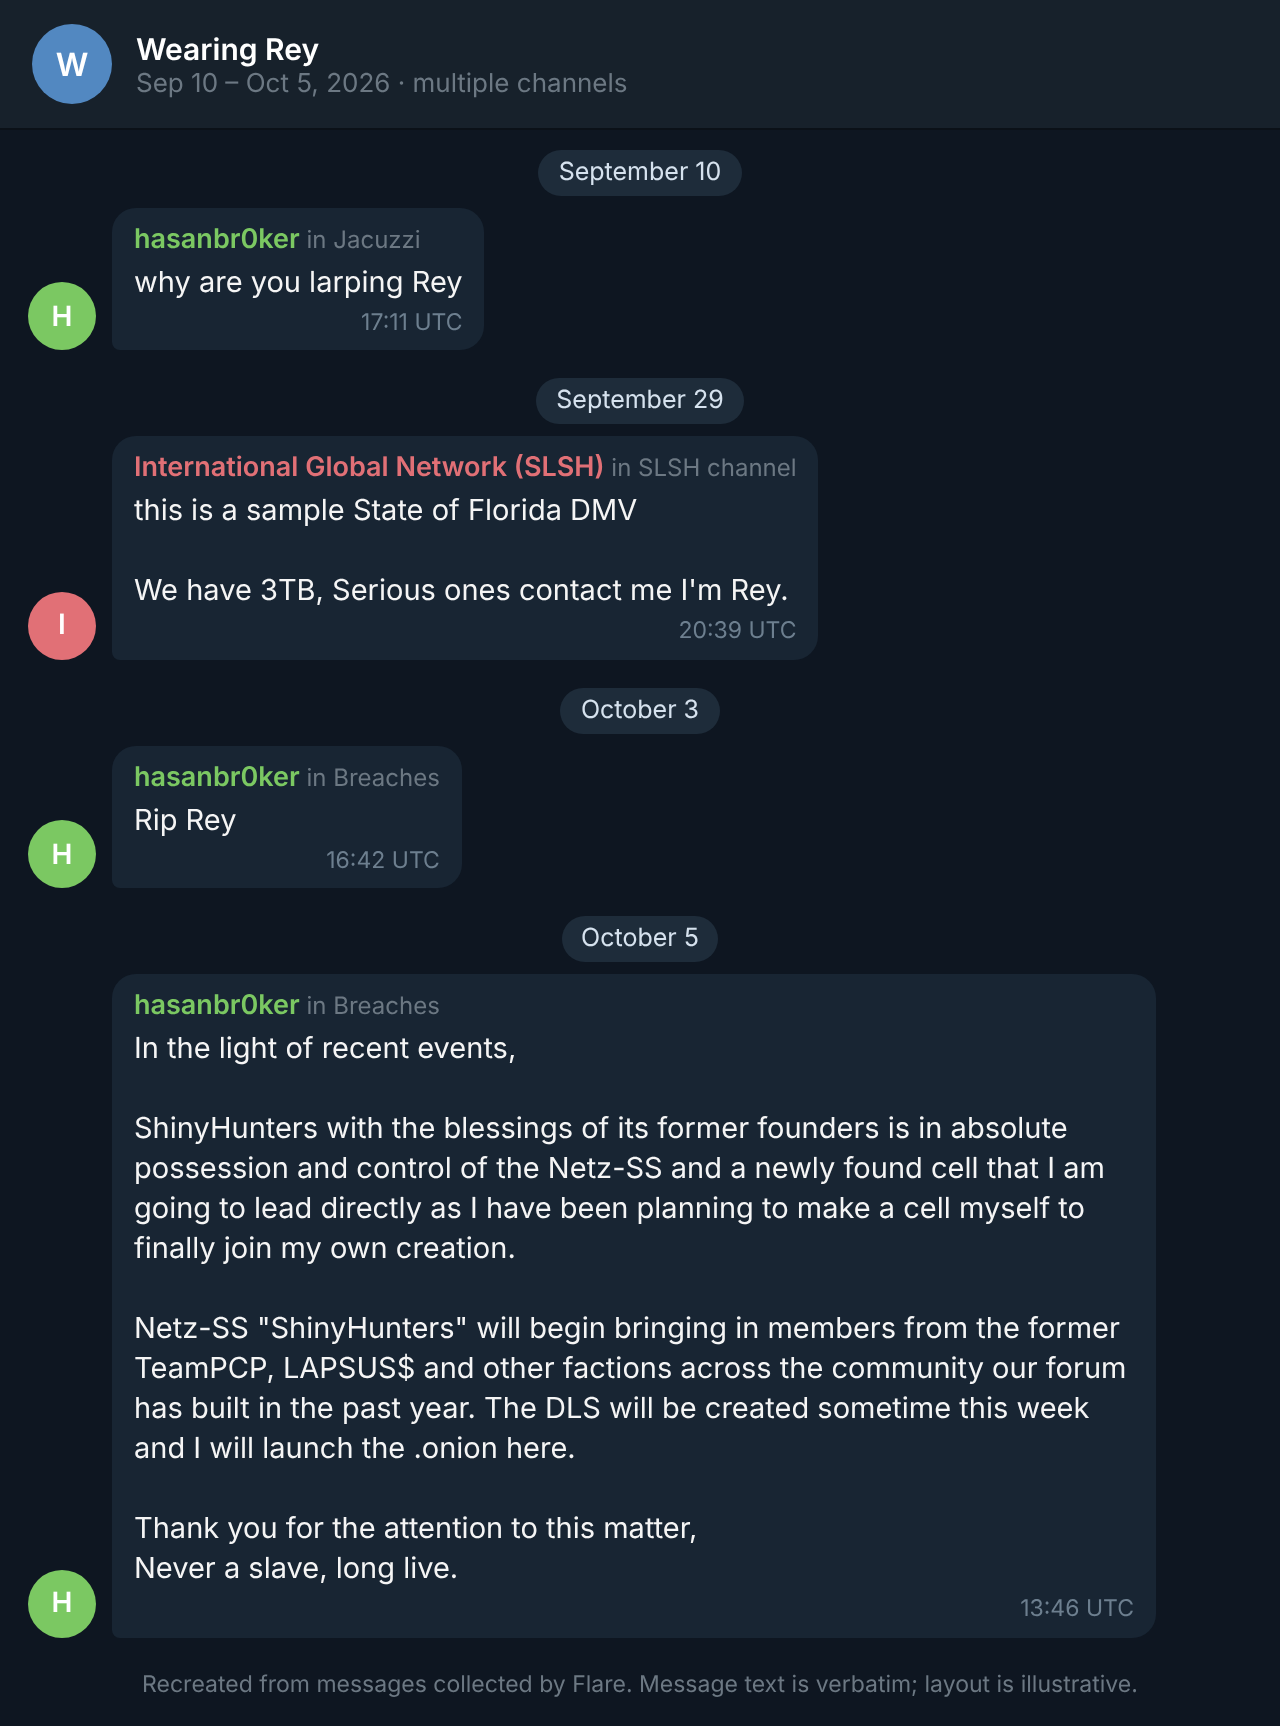
Rey was the loudest voice on the Telegram side, so when he went quiet, someone had to fill the space. In the thirty days before hasanbr0ker’s October 5 claim, people posted as Rey, called out others for pretending to be Rey, and then buried him.
| Date | Event | Source |
|---|---|---|
| Sep 10 | hasanbr0ker: "why are you larping Rey" | Flare |
| Sep 25 to 30 | SLSH channel (International Global Network) posts as Rey. Listed contact: @reyswap. Claim: "i'm Rey" |
Flare |
| Sep 28 | Unconfirmed source report: Rey in custody, Jordan law enforcement using his access | Arkem source |
| Sep 29 | hasanbr0ker again accuses an account of larping Rey | Flare |
| Oct 3 | Reuters reports the arrest; hasanbr0ker posts "Rip Rey" and a Netz-SS manifesto | Reuters, Flare |
| Oct 5 | hasanbr0ker announces a new ShinyHunters-branded cell "with the blessings of its former founders"; promises a data leak site that week | Flare |
| Oct 7 | Krebs publishes on Rey and the franchise | KrebsOnSecurity |
Someone was posting as Rey in the last week of September, while my source says Rey was already in custody. By calling out Rey impersonators throughout September, hasanbr0ker set himself up as the one policing the name. He then eulogized Rey and claimed the name himself.
The Arrest Playbook
The disputes kept returning to one phrase: official channel.
Across these disputes, I kept seeing the same moves.
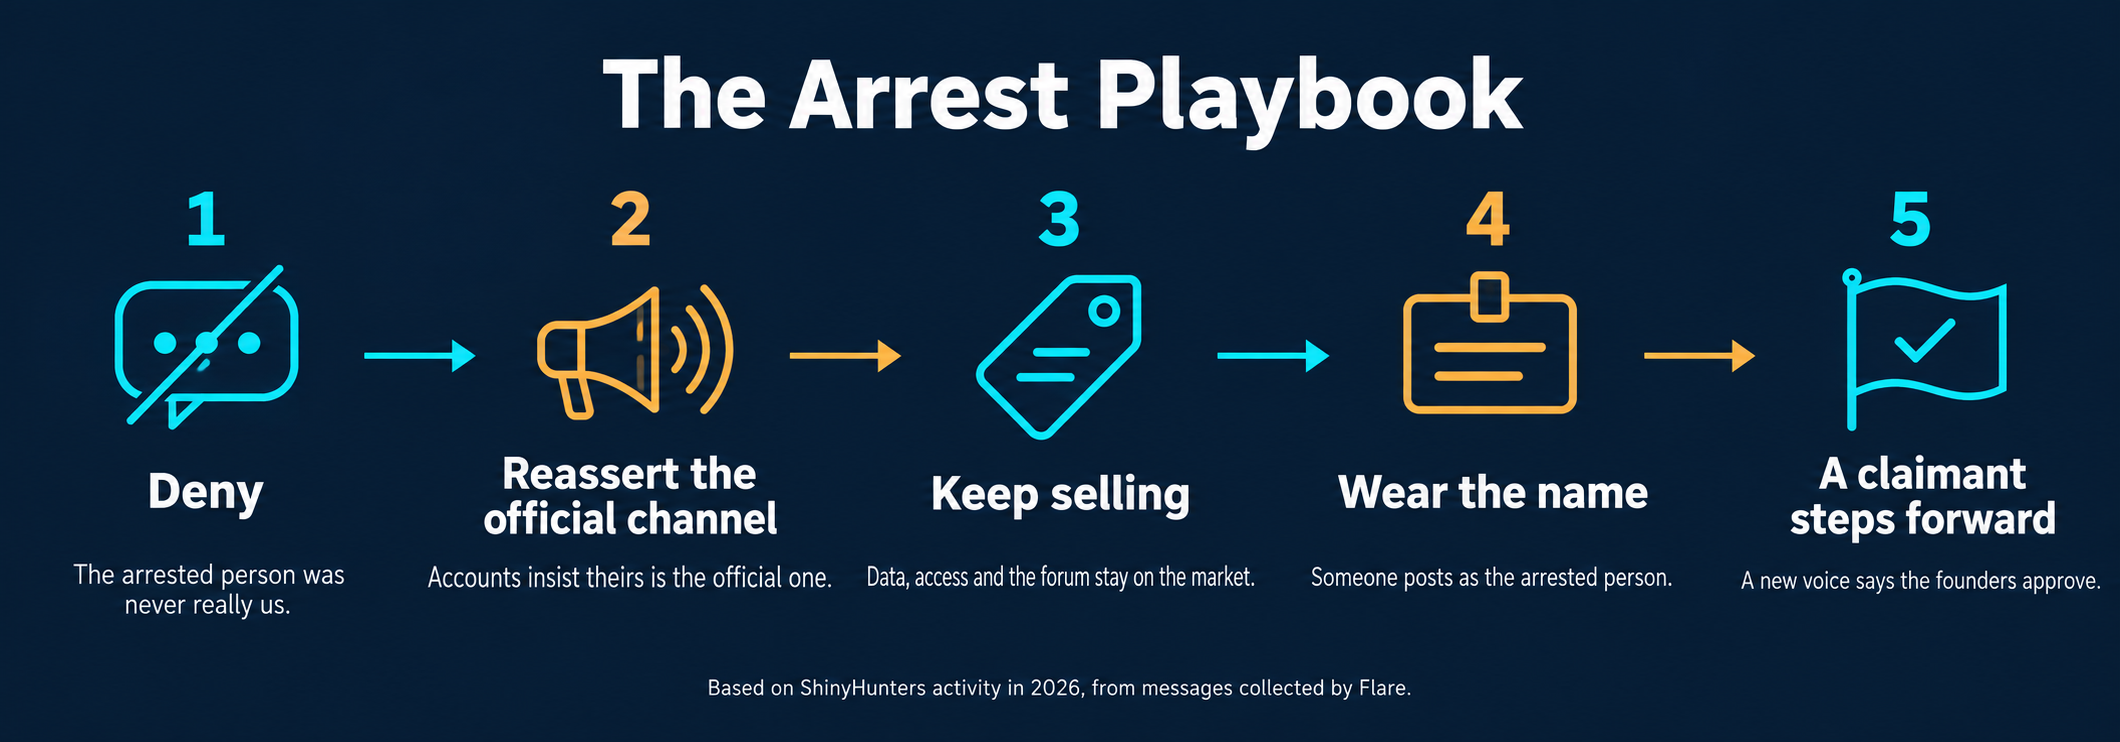
- Deny. The arrested person was never really us.
- Reassert the official channel. Accounts insist that theirs is the official one.
- Keep selling. Data, access and the forum itself stay on the market.
- Wear the name. Someone posts as the arrested person.
- A claimant steps forward. A new voice says the founders approve.
On October 5, hasanbr0ker stepped forward to claim the name. I expect the promised leak site to recycle old data. When it goes up, compare the victims against the existing ledger before you count a single new one.
What I Believe, and How Sure I Am
The keys and statements I examined do not establish who controls the ShinyHunters name today. E80C was exposed, the F495 copy I tested lacks the claimed certifications from the 2020 keys, and the altered June repost fails verification.
| Finding | Weight | Note |
|---|---|---|
| E80C exposed before the Dec 17 signature | High | Owner’s own statement, BleepingComputer |
| Examined F495 copy has no certification from the 2020 keys | High | My Oct 6 test |
| Altered June 12 repost fails verification | High | Bad signature |
| Hollow alias appears in breachforums[.]rs ownership claims | Moderate | Alias overlap; identity unresolved |
| hasanbr0ker has founder approval | Low | Self-claim, unsigned, uncorroborated |
I rate hasanbr0ker’s claimed “blessings of its former founders” at low confidence. He offered no signature, and I have not found independent corroboration of the claimed approval. The remaining founders may really have approved his new cell. The October 5 post does not establish that.
If Jordanian law enforcement holds Rey’s access, it could be behind some of the late-September Rey posts rather than an impersonator. I have no evidence for that, but I would not rule it out either.
Closing
ShinyHunters isn’t a group anymore so much as a brand people fight over. The keys that were supposed to prove who speaks for it leaked, multiplied, or were forged. The people who held them are arrested, missing or accused of turning on each other. And every time someone goes down, someone new steps up and says the founders approve.
Watch for the Netz-SS leak site and for any statement signed with 74D8, the key posted on March 20. When either shows up, check it against what you’ve read here before you repeat it. I’ll lay out the infrastructure behind all of this in a follow-up with Flare.
Until then, stop treating a signature from this crowd as proof of who sent it.
Sources and Acknowledgments
Thanks to Flare for access to its dark web and Telegram collection, which surfaced the October 5 claim, the September Rey posts and the forum sale listings, and to Authentic8, whose Silo platform I used for this research.
- Brian Krebs, KrebsOnSecurity, October 7, 2026. ShinyHunters Extorted Boeing Spin-Off Prior to Arrests
- Reuters, October 3, 2026. Key ShinyHunters hacker detained in Jordan is cooperating, sources say
- BleepingComputer, January 10, 2026. BreachForums hacking forum database leaked, exposing 324,000 accounts
- The Register, January 12, 2026. Infamous BreachForums forum breached, spilling data on 325K users
- The Hunter’s Ledger, April 17, 2026. ShinyHunters Data Leak Site at 91.215.85.22 — Infrastructure, Victims, and Attribution
- Jon DiMaggio, ShinyHunters profile, Analyst1, February 25, 2026.